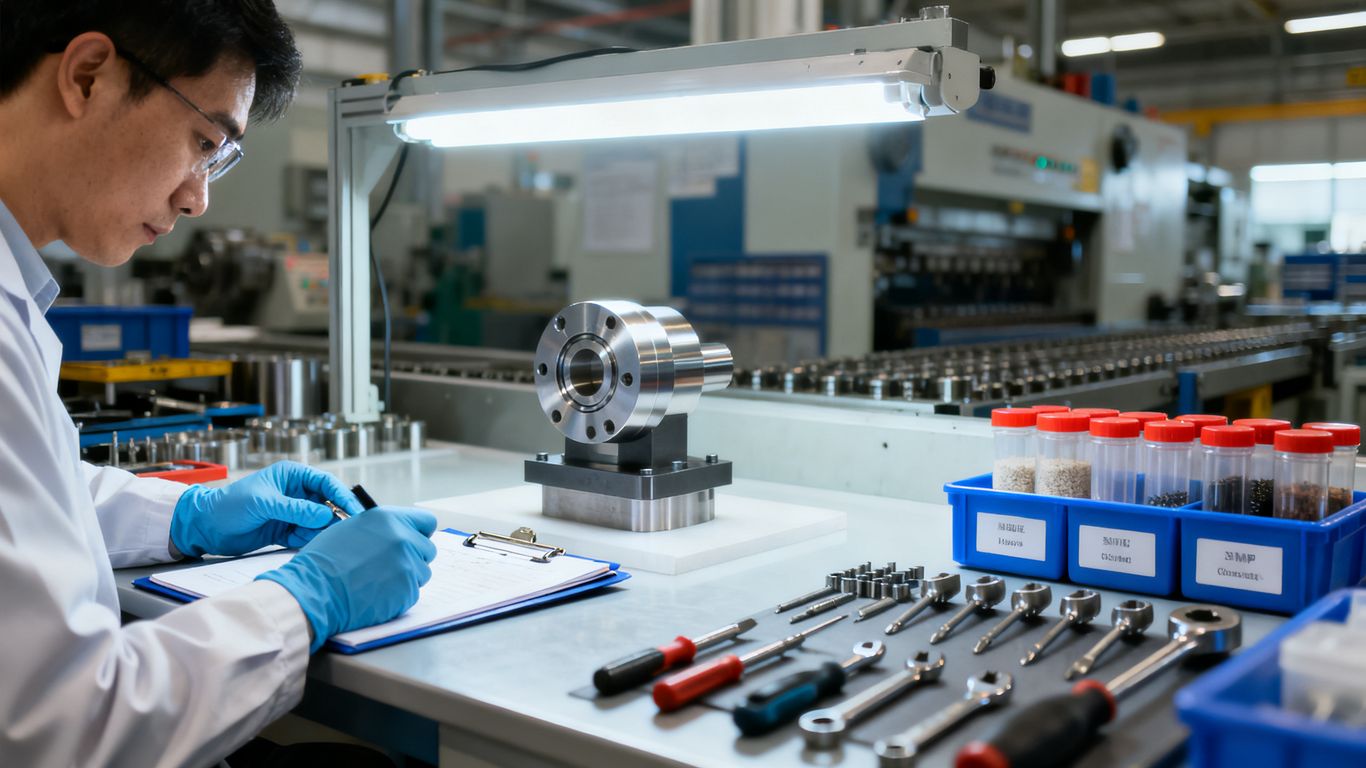
Quality control gives an organization a way to check whether its products or services meet defined requirements before problems spread. It can help identify hazards, reduce inconsistency, and create a record of how decisions were made. These practices may support a stronger response if a defect or complaint arises, but they cannot eliminate every risk or replace sound legal and operational judgment.
Preventing defects before they cause harm
The earlier a defect is detected, the more options an organization may have to keep it from reaching customers. Checks during design, production, or service delivery can reveal a failure while it is still limited to a test, a work order, or a small batch. This early intervention can reduce the chance that a preventable problem will cause injury, property damage, or disruption.
Reducing exposure to negligence and warranty claims
A consistent control process can help show that an organization took reasonable steps to identify and address foreseeable quality concerns. Written requirements, review points, and escalation procedures make it easier to see whether staff followed the intended process and how exceptions were handled. These records may inform a claim review, though they do not determine legal responsibility on their own.
Supporting consistent products and services
Customers reasonably expect products and services to meet stated requirements from one order or interaction to the next. Defined checks help reduce variation between teams, shifts, suppliers, and locations. A broader overview of quality control in production likewise discusses the role of defined processes and inspection in maintaining consistency.
Understanding the limits of quality control
No inspection plan can find every defect, and a test only speaks to the conditions and sample it covers. A process that worked yesterday may also become unreliable after a design change, equipment issue, or shift in materials. Quality control is therefore one part of risk management, alongside competent decision-making, clear communication, and appropriate legal review.
Where liability risks emerge
Liability can arise at many points between an initial requirement and a customer’s use of a product or service. A flaw may originate in a design assumption, enter through a supplier, or appear during routine work. Understanding where failures can occur helps organizations choose controls that address actual exposures rather than relying on a final inspection alone.
Design and specification failures
A design can meet its stated specification and still be unsuitable for its intended use if important conditions were overlooked. Requirements that are vague, incomplete, or inconsistent may also lead teams to make different assumptions about safety, performance, or acceptable variation. Reviewing intended use, foreseeable misuse, and applicable requirements before release can expose gaps while changes are still manageable.
Supplier and incoming-material problems
Purchased materials and components may vary, arrive damaged, or fail to meet agreed requirements. A supplier’s past performance is useful context, but it does not guarantee that every shipment is conforming. Organizations can reduce uncertainty by defining acceptance criteria, checking higher-risk inputs, and documenting how nonconforming deliveries are handled.
Production and service-delivery errors
Even a well-designed product can become unsafe or unreliable if a production step is skipped, equipment is out of tolerance, or instructions are misunderstood. Service organizations face similar exposure when required steps are missed or work is performed inconsistently. Clear process controls should identify which tasks are critical and how staff should respond when the expected conditions are absent.
Packaging, labeling, and communication gaps
A product may be manufactured correctly yet create risk if its packaging, warnings, or instructions are incomplete or confusing. Service communications can present similar problems when limitations, conditions, or next steps are not explained clearly. Organizations should review customer-facing information alongside the product or service itself, rather than treating communication as an afterthought.
Core controls that reduce risk
Effective controls connect requirements to observable actions. They explain what must be achieved, where checks occur, who is responsible, and what happens when results fall outside the acceptable range. A control is useful when employees can apply it consistently and managers can tell whether it is working.
Setting measurable quality standards
Standards should describe outcomes that can be evaluated, not just broad aims such as “good quality.” Depending on the work, a requirement might specify a tolerance, a required document, a service response step, or a condition that prevents release. Common elements of a measurable standard include:
- The characteristic or task that must meet the requirement.
- The acceptable range or pass/fail condition.
- The method and timing for checking it.
- The person responsible for review and escalation.
Together, these elements make expectations easier to teach and apply. They also reduce disputes about whether a result was acceptable and provide a practical basis for deciding when work should pause, be corrected, or receive further review.
Inspecting and testing at critical points
Inspection is most useful when it is placed where it can inform a decision. An incoming-material check may prevent a known issue from entering production, while an in-process test can catch a deviation before additional units are affected. Final inspection still has a role, but it should not carry the entire burden of finding problems created upstream.
Training employees on procedures and escalation
Written procedures do little good if employees do not understand the tasks, limits, and reporting paths they describe. Training should cover not only the normal sequence of work but also how to recognize a deviation and whom to notify. Refresher instruction is particularly useful when a procedure, role, or equipment setup changes.
Qualifying suppliers and monitoring changes
Supplier controls can include an initial assessment, clear purchase requirements, and review of incoming performance. Organizations should also pay attention to changes in materials, manufacturing methods, ownership, or delivery conditions that could affect conformance. Monitoring does not mean every supplier needs identical oversight; the level of review should reflect the potential impact of a failure.
Records that support defensible decisions
Records help reconstruct what happened, what information was available, and who made a decision. Their value depends on accuracy and context: a form marked “pass” is less useful if it does not identify the item, requirement, method, or reviewer. A well-designed record system supports both routine improvement and a careful response to questions later.
Documenting inspections, tests, and approvals
Inspection and test records should identify the subject checked, the relevant criteria, the result, and the person or system that recorded it. When results fall outside limits, the record should also show what action followed and whether a release or approval was withheld. Complete entries make it possible to distinguish a documented decision from an assumption made after the fact.
Maintaining traceability for products and materials
Traceability helps an organization connect a finished product or service to the materials, batches, work steps, or personnel associated with it. The appropriate level depends on the product and the likely consequences of a failure. When a concern appears, useful traceability can narrow the scope of review and help identify what else may be affected.
Controlling procedures and record revisions
Employees need access to current procedures, and an organization needs to know which version applied when work was performed. Revision controls should identify changes, approvals, effective dates, and how outdated copies are removed or marked. This prevents teams from following conflicting instructions and makes later review more reliable.
Protecting records while meeting retention requirements
Quality records may contain sensitive business or personal information, so access should be appropriate to the record’s purpose. Retention periods should reflect applicable laws, contracts, and operational needs, with a consistent process for secure disposal when records are no longer required. Legal holds or anticipated disputes may require preservation beyond routine schedules, so responsible teams should have a clear escalation path.
Responding to defects and potential claims
A suspected defect calls for prompt, organized action. The first decisions may involve safety, customer exposure, and whether related work should continue. Organizations should preserve the facts while avoiding premature conclusions about cause or responsibility.
Containing affected products or services
Containment may involve pausing release, isolating inventory, stopping a service step, or identifying customers who may be affected. The response should be proportionate to the potential severity and informed by what is known at the time. Clear authority to hold or quarantine work can prevent uncertainty from turning into further exposure.
Investigating root causes and preserving evidence
An investigation should distinguish the observed problem from possible explanations for it. Relevant materials may include samples, equipment settings, work records, communications, and the procedure in effect at the time. Preserving those materials and recording when they were collected helps maintain a reliable basis for analysis.
Correcting problems and verifying corrective actions
A correction addresses the immediate issue; a corrective action seeks to prevent recurrence by changing the process or its controls. After changes are made, the organization should verify that they were implemented and that they reduce the problem under relevant conditions. Closing an action only because a form is complete can leave the underlying risk untouched.
Coordinating quality, legal, and customer communications
Quality teams can explain technical findings, while legal and customer-facing teams may help assess obligations and prepare appropriate communications. Coordination reduces the chance that different groups provide inconsistent accounts or make unsupported assurances. Communications should be timely, factual, and reviewed through the organization’s established escalation process.
Building an effective quality control program
A quality control program should fit the organization’s products, services, and operating conditions. It need not treat every process as equally risky; it should concentrate attention where failures could have the greatest consequences. Regular review helps keep controls useful as the organization and its obligations change.
Prioritizing controls by severity and likelihood
Risk prioritization considers both how likely a failure is and what could happen if it occurs. A low-frequency hazard with serious consequences may deserve stronger controls than a common but minor inconvenience. Teams should document the basis for their priorities and revisit it when new evidence changes the assessment.
Assigning clear ownership and escalation paths
Each important control needs an owner who understands the expected work and has authority to act when results are unacceptable. Employees should know how to report concerns, where the concern goes next, and who can stop work or delay release. Clear escalation reduces the chance that an issue will be ignored because responsibility is assumed to belong to someone else.
Auditing processes and reviewing performance indicators
Audits can test whether procedures are being followed and whether they remain practical in day-to-day work. Performance indicators, such as recurring defects, rejected materials, or overdue corrective actions, can signal patterns that individual incidents might hide. Indicators should prompt investigation rather than serve as targets that encourage incomplete reporting.
Updating controls as products, regulations, and risks change
A control that fits one product version or operating environment may not remain adequate after a change. Organizations should review procedures when designs, suppliers, equipment, regulations, or customer expectations shift, and determine whether training and records need updating as well. This ongoing attention keeps quality control tied to current conditions instead of leaving it as a static set of documents.
